
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
- Triple validation: technical, pedagogical, sectoral.
- Minimum rating 4.8/5 over the last 12 sessions.

Describe your need, get a tailored program and a pre-filled quote in 3 min. A 100% free call with an advisor.
Very demanding course · Expertise required

Trusted by — schools, companies and industrial groups
41,306 programs · 25 countries
Every program built with a dedicated engineer






Companies: Aptar, ArcelorMittal, Equans, EDF, Ubisoft, Microsoft and Atos.
Program
Immersion in passive and active enumeration methods to identify target assets, use of OSINT tools like Maltego and Recon-ng to map digital footprints, customized scans with Nmap scripting engine and Masscan to detect vulnerable services, exercises on real company cases with result analysis, production of a preliminary reconnaissance report exploiting public and private data to simulate a sophisticated attack.
Practical exploitation of advanced OWASP Top 10 flaws such as SSRF, IDOR, and insecure deserialization, configuration of Burp Suite Pro to intercept and modify HTTP/S traffic, automation of scans with OWASP ZAP and Nuclei to detect recent CVEs, manual tests on DVWA and Juice Shop applications with custom payloads, development of Python scripts for targeted fuzzing, generation of proof-of-concept exploits to demonstrate business impact in a professional context.
Targeted attacks on network protocols such as SMB, RDP, and SNMP using EternalBlue and advanced Metasploit modules, use of RouterSploit for router and IoT pentesting, vulnerability scans with Nessus and OpenVAS integrated into CI/CD workflows, lateral pivoting exercises via SSH and Socks tunnels, simulation of attacks in a VMware lab with Windows/Linux machines, development of quantified risk metrics to prioritize enterprise fixes.
Deployment of persistent beacons with Cobalt Strike to maintain access, privilege escalation techniques via kernel exploits and Active Directory misconfigurations, PowerShell Empire scripting for lateral movement and credential dumping, simulated data exfiltration using DNS tunneling, practical cases on complex AD environments, creation of custom evasive payloads against EDRs, analysis of traces for stealth and covering tracks in professional audits.
Drafting executive reports with Dradis and Faraday to structure findings, calculation of CVSS v4 and EPSS scores for prioritization, precise hardening recommendations with mitigation PoCs, simulations of post-remediation re-tests, workshops on GDPR/ISO 27001 compliance, oral presentation of the red thread project to peers, issuance of certificates and personalized action plan to integrate these skills into the enterprise upon return.
The Training Security Testing - Auditing Critical Vulnerabilities in the Enterprise program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.
The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.
Equipment required
For the smooth delivery of the Training Security Testing - Auditing Critical Vulnerabilities in the Enterprise program, the following equipment is required:
For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.
Skills assessment methods
Assessment of skills acquired during the Training Security Testing - Auditing Critical Vulnerabilities in the Enterprise program is performed through:
Program accessibility
Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.
Enrollment terms and lead times
Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.
The Learni story
Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.
Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
You meet the trainer beforehand
30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.
Content tailored to your context
No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.
Continuous quality follow-up
Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.
A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
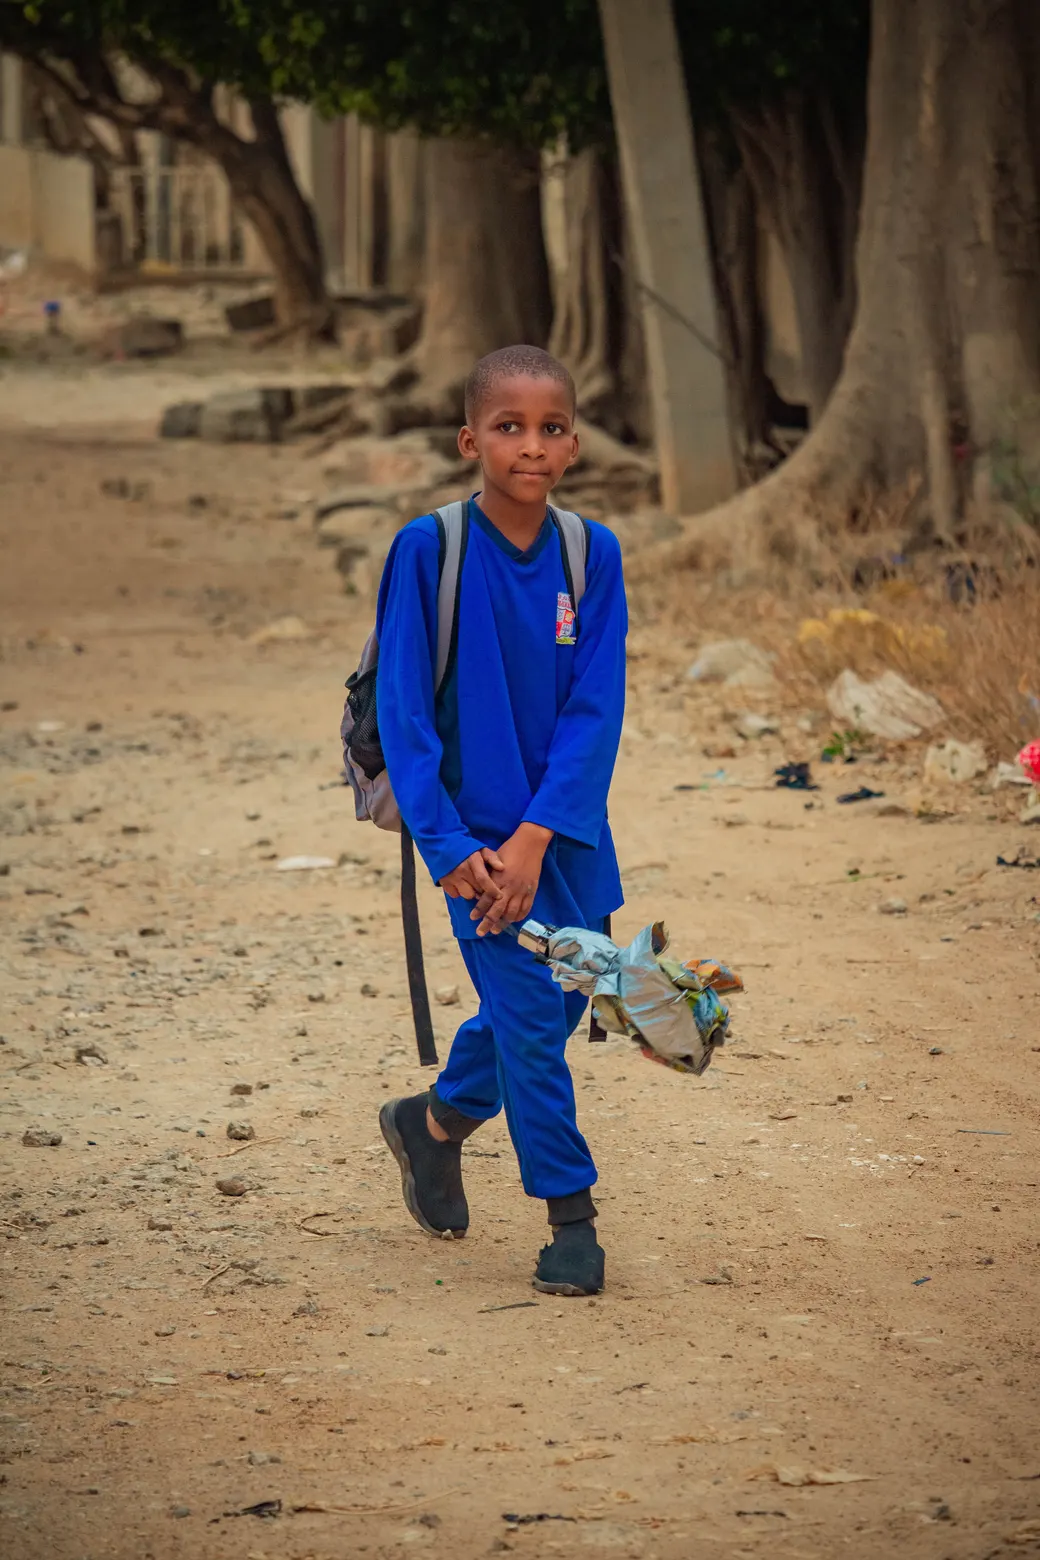
A school kit donated to a child for every training booked
To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.
30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.
 Security standards & governanceIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Cybersecurity fundamentalsIndustry-certifiedCybersecurity fundamentalsIndustry-certified
 Cybersecurity fundamentalsIndustry-certified
 Application securityIndustry-certifiedApplication securityIndustry-certified
 Application securityIndustry-certifiedNetworking & telecomsIndustry-certified
 Networking & telecomsIndustry-certified
 Networking & telecomsIndustry-certified
Available on-site and remotely. Pick your city to see the local training center.
We will call +1 (United States) 🇺🇸 — change the country code on the left if your number is from elsewhere.