
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
- Triple validation: technical, pedagogical, sectoral.
- Minimum rating 4.8/5 over the last 12 sessions.

Describe your need, get a tailored program and a pre-filled quote in 3 min. A 100% free call with an advisor.
Very demanding course · Expertise required

Trusted by — schools, companies and industrial groups
41,115 programs · 25 countries
Every program built with a dedicated engineer






Companies: Aptar, ArcelorMittal, Equans, EDF, Ubisoft, Microsoft and Atos.
Program
Rapid installation of Semgrep in an expert environment, CLI configuration and IDE integration, exploration of the official rules registry on concrete projects, writing of first pattern rules to detect data leaks and SQL injections, practical exercises on enterprise legacy code, analysis of results with precision metrics, production of initial actionable reports for security teams.
Deep dive into advanced YAML syntax for multi-language rules, mastery of metavariables and semantic capture to minimize false positives, creation of custom rules detecting OWASP Top 10 in JavaScript and Python, collaborative workshops on real enterprise cases, validation with Semgrep unit tests, performance optimization via focus-mode and exclusions, generation of deliverables ready for certifying audit.
Configuration of Semgrep in popular CI/CD pipelines like GitHub Actions and GitLab CI, deployment of automated scans on massive monorepos, management of pre-commit hooks for instant feedback, exercises on integration with SonarQube and other SAST tools, simulation of real-time breaches with rapid remediation, tuning of alert thresholds for DevOps teams, production of custom dashboards monitoring enterprise code health.
Development of tailor-made enterprise rules with Semgrep Pro features, exploration of ML for advanced contextual detection, workshops on performance tuning for millions of lines of code, case studies of major breaches avoided by Semgrep, development of scalable code security policies, final exercises on the ongoing project with presentation, post-training deployment plan for immediate ROI in the enterprise.
The Training Semgrep - Detecting Code Vulnerabilities in the Enterprise program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.
The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.
Equipment required
For the smooth delivery of the Training Semgrep - Detecting Code Vulnerabilities in the Enterprise program, the following equipment is required:
For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.
Skills assessment methods
Assessment of skills acquired during the Training Semgrep - Detecting Code Vulnerabilities in the Enterprise program is performed through:
Program accessibility
Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.
Enrollment terms and lead times
Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.
The Learni story
Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.
Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
You meet the trainer beforehand
30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.
Content tailored to your context
No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.
Continuous quality follow-up
Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.
A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
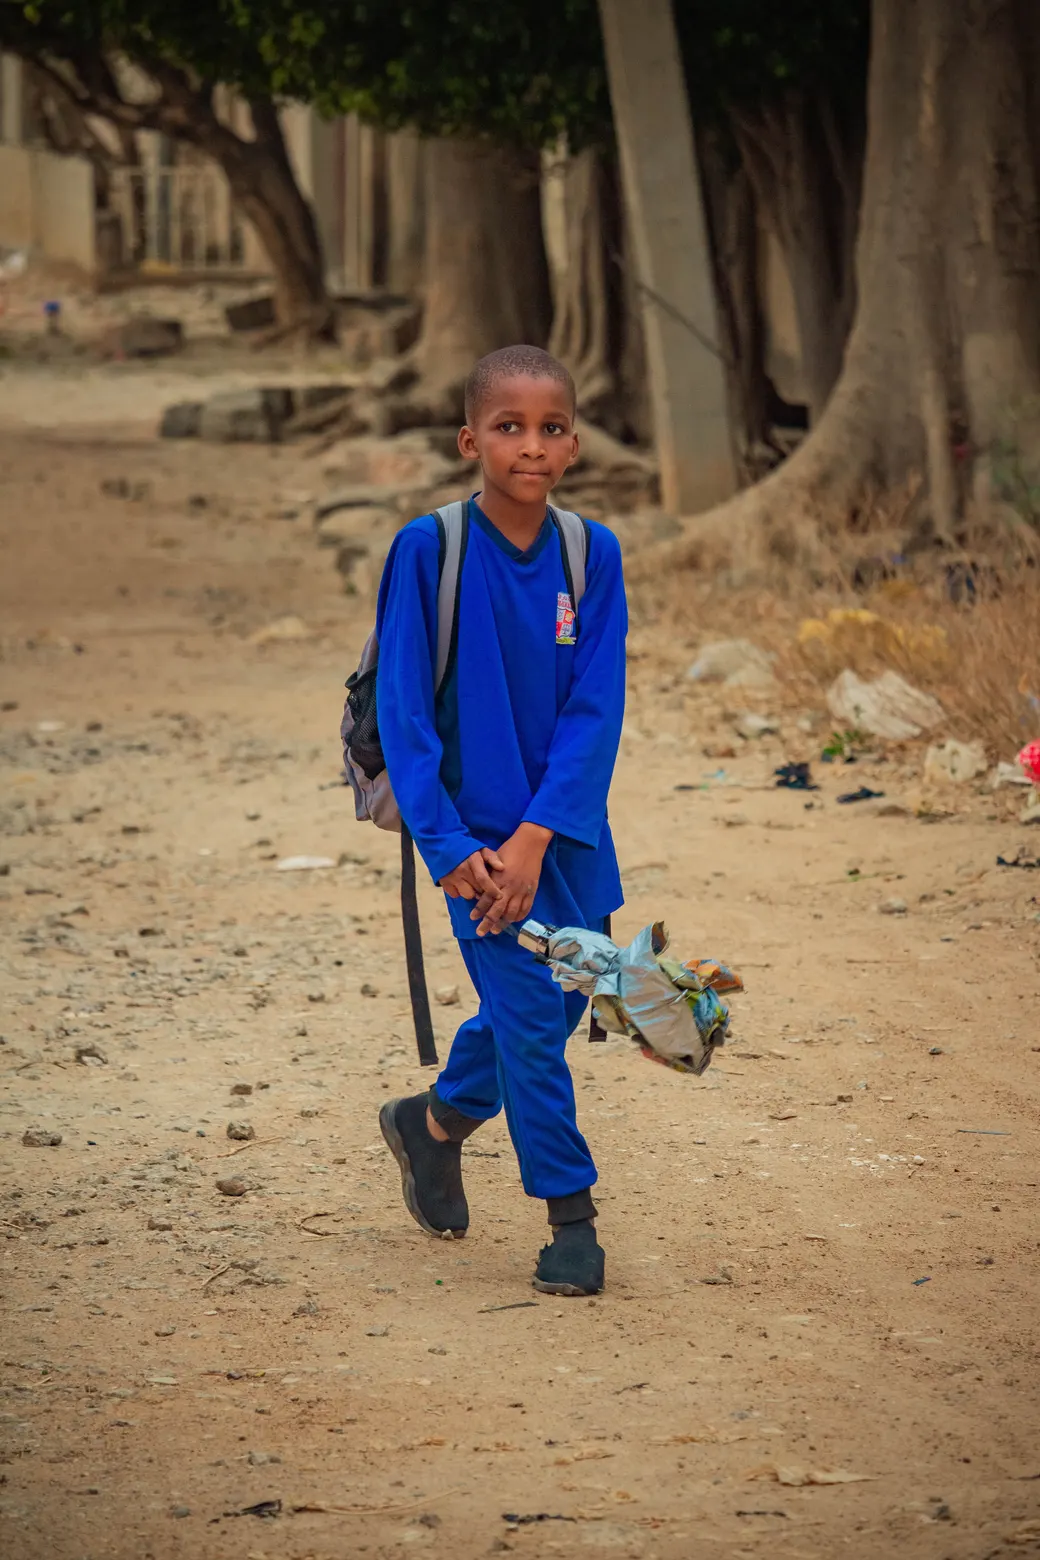
A school kit donated to a child for every training booked
To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.
30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.
 Pentesting & ethical hackingIndustry-certified
 Cloud computingIndustry-certified
 Programming LanguagesIndustry-certified
 Application securityIndustry-certified
 Application securityIndustry-certified
 Application securityIndustry-certified
 Programming LanguagesIndustry-certified
 Programming LanguagesIndustry-certified
 Programming LanguagesIndustry-certified
 DevOps & CI/CDIndustry-certifiedDevOps & CI/CDIndustry-certified
 DevOps & CI/CDIndustry-certified
 Backend & APIsIndustry-certified
 Backend & APIsIndustry-certifiedBackend & APIsIndustry-certified
Available on-site and remotely. Pick your city to see the local training center.
We will call +1 (United States) 🇺🇸 — change the country code on the left if your number is from elsewhere.