Training Security Maturity Assessment - Measure and Boost Cybersecurity

$5,775

  • 5 days
  • Onsite
  • 10 people max.
Ref: ICD674
10 people max.
$5,775
In-company rate: from $10,395 for the whole team
On-site and certification exam on quote
5 days
Onsite

Don't let this gap widen

Why this program matters

  • Without regular security maturity assessment, companies suffer an average of 2,5 breaches per year, costing 4,45 millions d'euros per incident according to IBM.

  • Immature teams lose 40% of time on ineffective alert responses, exposing them to GDPR fines up to 4% of CA.

  • In 2024, 68% of cyberattacks exploit undetected organizational weaknesses, hindering growth and ruining reputation.

  • Every quarter without security maturity assessment widens the gap with resilient competitors, directly threatening business viability.

Nawfel ABED, Learni trainer · Cybersecurity expert
Nawfel ABED

Learni trainer · Cybersecurity expert

73%productivity gap
×3cost of inaction
Flag of the United StatesBuilt for US teams
Payment by wire transferEnhanced confidentialityPerfect for companies with 50 to 500 employeesScheduling to fit any time zone

Trusted by — schools, companies and industrial groups

40,922 programs · 25 countries

  • Aptar
  • ArcelorMittal
  • Equans
  • EDF
  • Ubisoft
  • Microsoft

Every program built with a dedicated engineer

  • OpenAI
  • Anthropic
  • Mistral AI
  • NVIDIA
  • Google
  • Amazon Web Services
  • Microsoft Dynamics 365
  • Salesforce
  • ServiceNow
  • SAP
  • Oracle
  • Cisco
  • Fortinet
  • Palo Alto Networks
  • Aruba
  • VMware
  • Red Hat
  • Databricks
  • Snowflake
  • OVHcloud
  • Notion
  • AMD
  • Apple

Companies: Aptar, ArcelorMittal, Equans, EDF, Ubisoft and Microsoft.

Security Maturity Assessment training objectives

  • Master security maturity assessment models for professional certifying audits
  • Develop skills in security maturity assessment for companies
  • Design security maturity improvement plans tailored to organizational contexts
  • Implement security maturity assessment tools and methods in practice
  • Optimize security processes through structured and measurable assessments
  • Assess security maturity gaps and prioritize corrective actions
  • Produce actionable security maturity assessment audit reports for the company

Program

Security Maturity Assessment curriculum: 5 modules over 5 days

Module 1 : Fundamentals: Security Maturity Assessment Models (NIST, CMMI, ISO 27001)

Introduction to the main security maturity assessment frameworks such as NIST Cybersecurity Framework and CMMI for cybersecurity, comparative analysis of models suited to companies, practical exercises on identifying current maturity levels through real organizational cases, hands-on with free tools like the NIST CSF tool, development of an initial simplified diagnosis on a company scenario, with personalized feedback from the trainer to anchor essential concepts.

Module 2 : Methodology: Conducting a Complete Security Maturity Assessment (Questionnaires, Interviews)

Implementation of a structured methodology for security maturity assessment, design of targeted questionnaires and customizable evaluation grids, simulations of stakeholder interviews via role-play in remote format, use of collaborative tools like Microsoft Forms or Google Workspace to collect reliable data, initial processing of results with automated scoring, production of a preliminary report on a red thread company project, demonstrating immediate value for strategic decision-making.

Module 3 : Analysis: Assess Security Maturity Gaps and Identify Priority Risks

In-depth analysis of data collected during the security maturity assessment, mapping gaps by domain (governance, detection, response), prioritization of risks using heatmaps and quantitative scoring, exercises on real incident cases such as ransomware or data leaks, use of advanced tools like Excel or Power BI to visualize gaps, development of a priority action plan with estimated ROI, enhancing the credibility of your recommendations in the company.

Module 4 : Advanced Tools: Automate Security Maturity Assessment (CIS Controls, Scanners)

Exploration of professional tools for security maturity assessment such as CIS Controls Assessment Tool and open-source scanners (OpenSCAP, Lynis), configuration and execution of automated audits on provided virtual environments, integration of results with manual diagnostics, practical workshops on automation using basic Python scripts, tests on a simulated company case with real vulnerabilities, generation of interactive dashboards to track maturity evolution, highlighting your technical skills in a professional context.

Module 5 : Synthesis and Roadmap: Deploy an Improvement Plan Post-Security Maturity Assessment

Finalization of the complete security maturity assessment report with actionable recommendations and a 12-24 month roadmap, workshops on drafting proposals for management, simulations of presentations to an executive committee via videoconference, integration of KPI metrics to measure future progress, review of the red thread project with code review and optimization, delivery of a reusable certified template, preparing participants to certify their own assessments in the company with confidence and immediate impact.

How Security Maturity Assessment skills are assessed

  • Multiple-choice quiz to validate learning at the end of the training on models and tools
  • Continuous evaluation through practical exercises and red thread project
  • Defense of the security maturity assessment report in front of the expert trainer

How the Security Maturity Assessment course is taught

  • Lessons delivered by an active CISO expert trainer
  • Practical exercises on real company cybersecurity cases
  • Progressive red thread project throughout the training
  • Complete course materials provided to each participant

Security Maturity Assessment training: access and practical arrangements

The Training Security Maturity Assessment - Measure and Boost Cybersecurity program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.

The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.

Equipment required

For the smooth delivery of the Training Security Maturity Assessment - Measure and Boost Cybersecurity program, the following equipment is required:

  • Mac or PC computers, high-speed fiber internet, whiteboard or flipchart, projector or interactive touch screen (for remote sessions)
  • Training environments installed on workstations or accessible online
  • Course materials, hands-on exercises and complementary resources
  • Post-training access to materials and educational resources

For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.

* contact us for remote delivery feasibility** ratio varies depending on the program

Skills assessment methods

Assessment of skills acquired during the Training Security Maturity Assessment - Measure and Boost Cybersecurity program is performed through:

  • During training: case studies, hands-on labs and professional scenarios
  • End of training: self-assessment questionnaire and skills evaluation by the trainer
  • After training: completion certificate detailing acquired skills

Program accessibility

Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.

Enrollment terms and lead times

Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.

The Learni story

Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.

Our method

How Learni guarantees the quality of your Security Maturity Assessment training

Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.

Step 1

Rigorous trainer selection

Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.

  • Triple validation: technical, pedagogical, sectoral.
  • Minimum rating 4.8/5 over the last 12 sessions.
Step 2

You meet the trainer beforehand

30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.

  • Live briefing on goals and team context.
  • Veto right — we swap the trainer for free if needed.
Step 3

Content tailored to your context

No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.

  • Hands-on cases drawn from your stack and projects.
  • Program co-written then validated by your team.
Step 4

Continuous quality follow-up

Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.

  • NPS, knowledge quizzes and skills self-assessment.
  • Satisfaction guarantee: fully satisfied or free rework.

A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
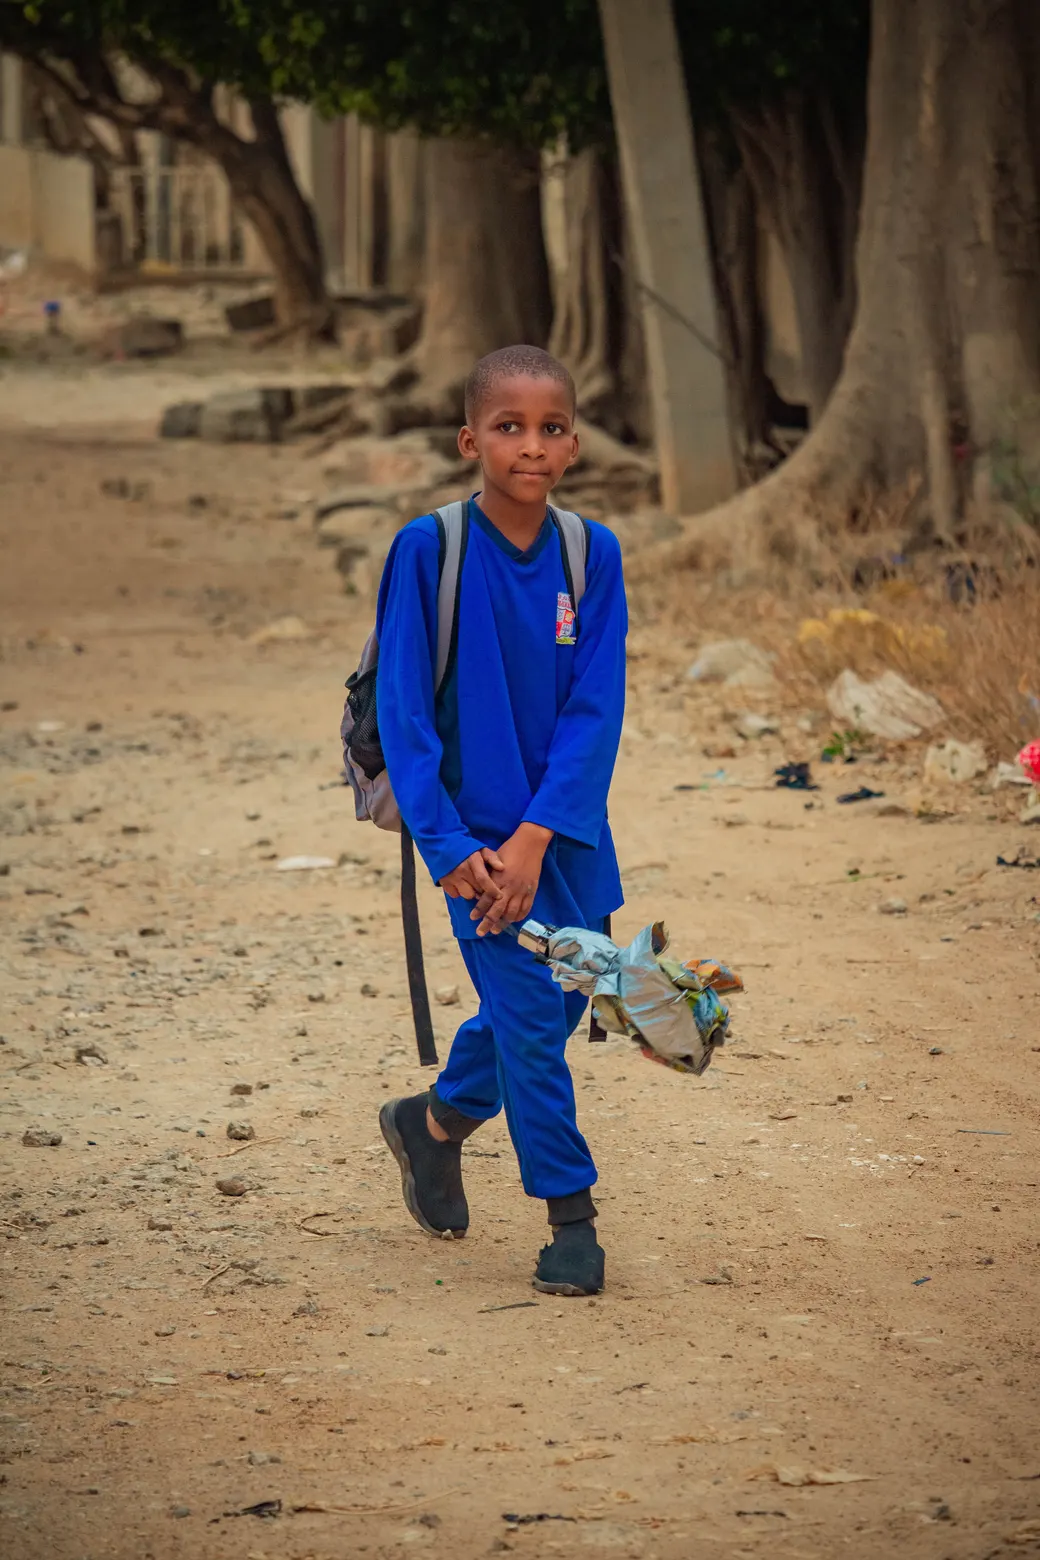
A child walking to school with a backpack
Our social commitment

A school kit donated to a child for every training booked

To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.

  • Backpack, notebooks and essential supplies
  • Distributed through our partner charities
  • Included, at no extra cost to you
Enroll and offer a kit
FAQ

Security Maturity Assessment: frequently asked questions

Which tools are used in Security Maturity Assessment training?+
Hands-on work runs on NIST, CMMI, ISO 27001, questionnaires, interviews and CIS Controls. Those tools come from the Security Maturity Assessment program itself, delivered on site over 5 days, so participants practise on the stack they will use at work.
What can participants do after Security Maturity Assessment training?+
They can master security maturity assessment models for professional certifying audits, develop skills in security maturity assessment for companies and design security maturity improvement plans tailored to organizational contexts. Those are the stated objectives of the Security Maturity Assessment program at Intermediate level, checked by the end-of-session assessment.
What does the Security Maturity Assessment program cover, day by day?+
Day 1: Fundamentals: Security Maturity Assessment Models (NIST, CMMI, ISO 27001). Day 2: Methodology: Conducting a Complete Security Maturity Assessment (Questionnaires, Interviews). Day 3: Analysis: Assess Security Maturity Gaps and Identify Priority Risks. Day 4: Advanced Tools: Automate Security Maturity Assessment (CIS Controls, Scanners). Day 5: Synthesis and Roadmap: Deploy an Improvement Plan Post-Security Maturity Assessment. The Security Maturity Assessment program runs over 5 days, delivered on site.
How is Security Maturity Assessment training assessed?+
Assessment relies on multiple-choice quiz to validate learning at the end of the training on models and tools, continuous evaluation through practical exercises and red thread project and defense of the security maturity assessment report in front of the expert trainer. Learni issues a completion certificate together with the individual assessment report at the end of the Security Maturity Assessment program, which an L&D team can file as evidence.
How much does Security Maturity Assessment training cost per participant?+
Security Maturity Assessment training costs $5,775 per participant. For an in-company team, the flat rate starts at $10,395 for the whole group, up to 8 people. The detailed quote, sent within one business day, adjusts the amount to the format and how far the syllabus is tailored to your team.
How long does Security Maturity Assessment training take?+
5 days, available live online (US time zones) or on-site at your offices. Half-day tracks spread over several weeks are possible so the team stays operational.
Who pays for Security Maturity Assessment training?+
Most US teams pay directly through their company L&D or training budget. Learni invoices in US dollars and accepts bank transfer (ACH/wire) or card, with volume pricing for teams. A purchase order is welcome.
What do participants need to know before Security Maturity Assessment training?+
Basic knowledge in cybersecurity, experience in audits or IT risk management.
Is a certificate issued after Security Maturity Assessment training?+
Yes. A Learni completion certificate is issued, along with the individual evaluation report. Learni is a certified training provider and prepares for third-party certifications, but does not award them itself.
Does Learni provide the equipment for Security Maturity Assessment training?+
No. A computer and a stable internet connection are required for each participant. Learni provides the learning platform, the trainer and all course materials.
Your professional training, anywhere

Let's build your Security Maturity Assessment learning path.

30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.
Reply within 24h · Vetted experts · USD invoicing · W-9 available
On-site & remote

Security Maturity Assessment training in your city

Available on-site and remotely. Pick your city to see the local training center.

Share in 2 clicks