
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
- Triple validation: technical, pedagogical, sectoral.
- Minimum rating 4.8/5 over the last 12 sessions.

Describe your need, get a tailored program and a pre-filled quote in 3 min. A 100% free call with an advisor.

25,751 programs · 25 countries
Every program built with a dedicated engineer






Companies: Aptar, ArcelorMittal, Equans, EDF, Ubisoft and Microsoft.
Dive into stealth and passive scans to identify hidden assets, hands-on with tools like Nmap using custom NSE scripts, Masscan for massive sweeps, integration of Shodan for industrial OSINT, exercises on vulnerable labs simulating real companies, creation of preliminary reports immediately actionable in professional missions, enhancing skills in the critical initial phase.
Targeted attacks on modern web applications, advanced Burp Suite Pro configuration for dynamic interceptions, SQL/NoSQL injection automation via custom SQLMap, advanced XSS/CSRF exploitation with obfuscated payloads, concrete cases from recent OWASP Top 10, development of custom Metasploit modules, delivery of functional exploits tested in your lab environment, boosting efficiency in enterprise audits.
Deep penetration of SMB, RDP, LDAP protocols via expert Metasploit modules, chaining exploits like EternalBlue-WannaCry recreations, bypassing firewalls/IDS with evasion techniques, using Cobalt Strike for stealthy C2, simulations of lateral movement attacks on Active Directory, practical exercises on corporate VMs, generation of stable persistent shells, strengthening skills for critical infrastructure pentests.
Root/admin privilege escalation techniques post-breach, credential extraction via advanced Mimikatz, internal pivoting with PowerShell Empire beacons, encrypted data exfiltration without detection, persistence via schtasks/registry backdoors, case studies of real breaches like SolarWinds, development of custom scripts for automations, production of documented post-exploit artifacts, essential for professional red team missions.
Audit synthesis with Dradis for impactful executive reports, integration of findings into MITRE ATT&CK frameworks, development of pentest automation pipelines via Docker/Ansible, review of the complete red thread project, expert CTF simulations, delivery of a certifying deliverables portfolio, focus on business-aligned remediation, preparing for OSCP+ certifications and elite careers in enterprise cybersecurity.
The Training Penetration Testing - Exploiting Critical Vulnerabilities program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.
The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.
For the smooth delivery of the Training Penetration Testing - Exploiting Critical Vulnerabilities program, the following equipment is required:
For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.
Assessment of skills acquired during the Training Penetration Testing - Exploiting Critical Vulnerabilities program is performed through:
Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.
Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.
Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.
Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.
No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.
Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.
A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
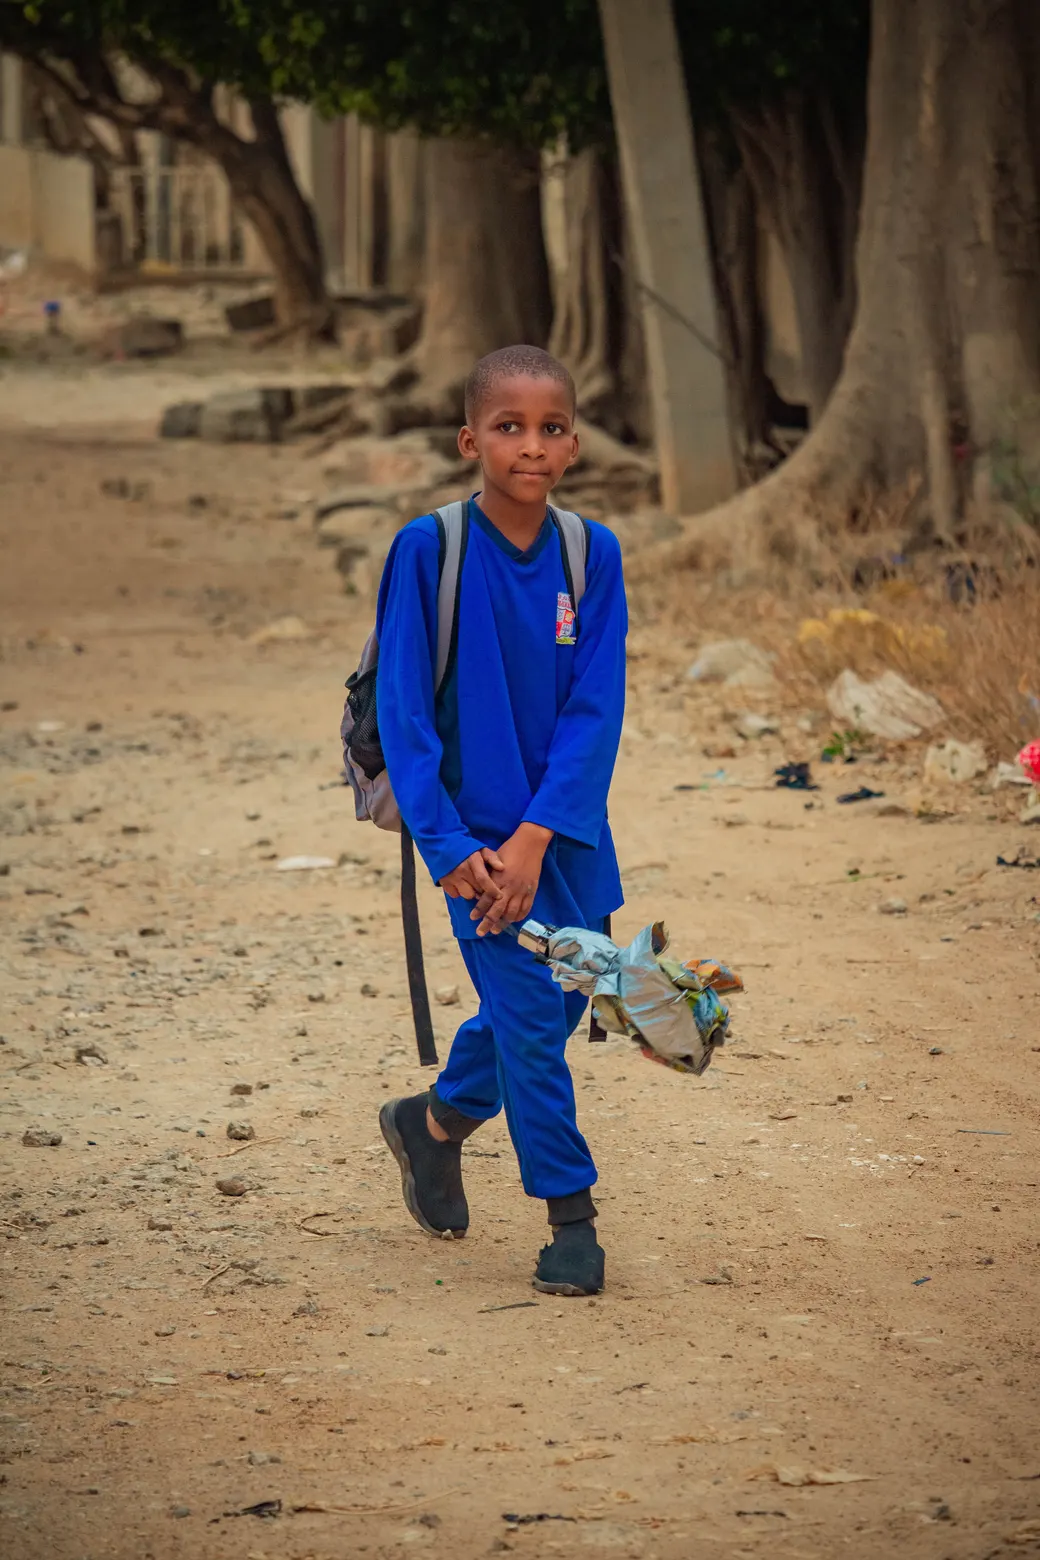
To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.
30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Security standards & governanceIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Cybersecurity fundamentalsIndustry-certifiedCybersecurity fundamentalsIndustry-certified
 Cybersecurity fundamentalsIndustry-certified
 Application securityIndustry-certifiedApplication securityIndustry-certified
 Application securityIndustry-certifiedNetworking & telecomsIndustry-certifiedNetworking & telecomsIndustry-certified
 Networking & telecomsIndustry-certified
Available on-site and remotely. Pick your city to see the local training center.
We will call +1 (United States) 🇺🇸 — change the country code on the left if your number is from elsewhere.