
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
- Triple validation: technical, pedagogical, sectoral.
- Minimum rating 4.8/5 over the last 12 sessions.

Describe your need, get a tailored program and a pre-filled quote in 3 min. A 100% free call with an advisor.

1 seat held for the next session
Request a call back and an advisor reaches you within 24 business hours, Monday to Saturday.
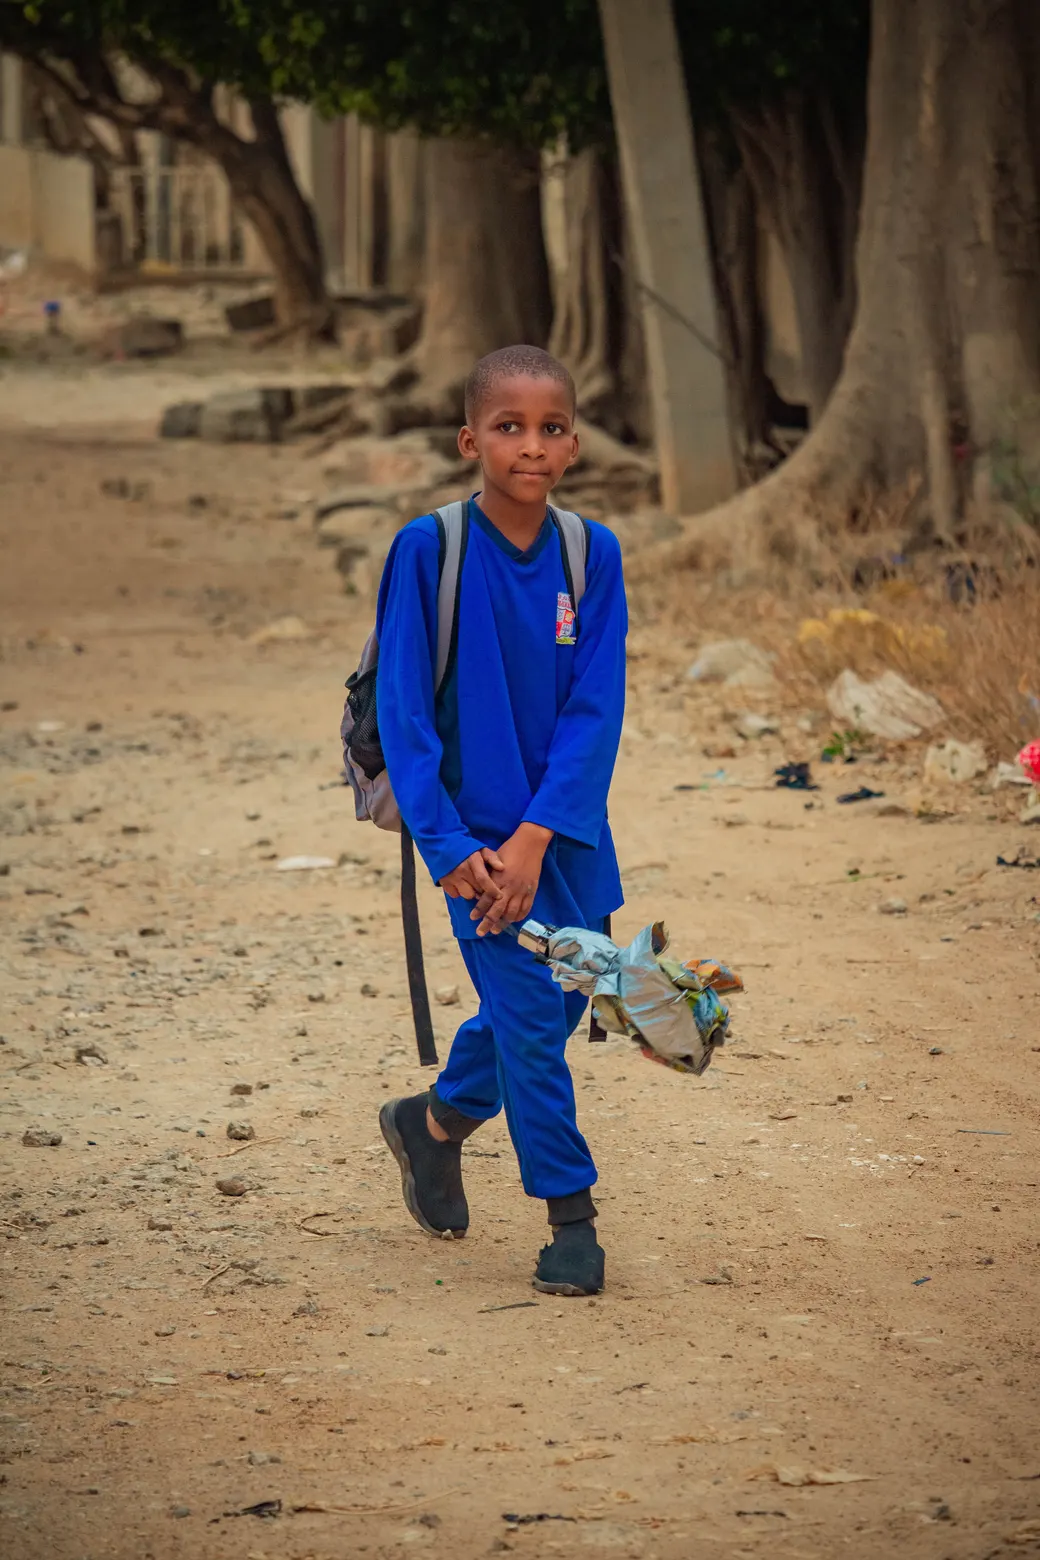
To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.
Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.
Don't let this gap widen
Without mastering Bug Bounty 2026, hotel sites exposed to attacks suffer 30% annual client data leaks according to Verizon DBIR, resulting in GDPR fines up to 4% of revenue, or millions of euros lost for tourism chains.
IT managers in hospitality risk mass layoffs after incidents, and company reputation collapses with negative traveler reviews.
Careers stagnate without cybersecurity skills, and bounty opportunities slip away.
Invest in beginner training to protect assets and boost professional expertise starting today.
Discover the essential principles of Bug Bounty 2026 through platforms dedicated to the tourism sector, explore engagement rules for hotels and restaurants, install tools like free Burp Suite, practice reconnaissance on vulnerable sites via guided exercises, analyze real cases of reservation data leaks, produce your first simple bug report, consolidate basics for secure corporate hunts.
Dive into Bug Bounty 2026 reconnaissance techniques applied to restaurants, use OWASP ZAP for passive scans of hotel web applications, identify sensitive endpoints via tourism-adapted Google Dorks, simulate audits of travel e-commerce sites, train on virtual labs for common vulnerabilities, generate target architecture maps, integrate findings into professional certified reports.
Master XSS attacks in the Bug Bounty 2026 context for hotel sites, configure Burp Suite to intercept reservation form requests, test payloads adapted to tourism client interfaces, exploit vulnerable reflections via practical exercises, analyze GDPR impacts of session leaks, draft detailed Proofs of Concept, apply immediate remediations to secure restaurant businesses.
Attack SQL injections via Bug Bounty 2026 on tourism reservation databases, deploy SQLMap to automate hotel data extractions, bypass weak authentications on check-in forms, practice on realistic restaurant challenges, assess risks of client PII exposure, produce quantified impact reports, integrate server hardening best practices.
Optimize Bug Bounty 2026 hunts with a focus on tourism reward monetization, structure professional HackerOne reports for hotels, review personal bug portfolios via peer review, simulate submissions to restaurant programs, calculate ROI of acquired skills, conclude training with a complete vulnerability final project, receive certification for enterprise security skills.
The Training Bug Bounty 2026 - Hunt Vulnerabilities to Secure Tourism program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.
The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.
For the smooth delivery of the Training Bug Bounty 2026 - Hunt Vulnerabilities to Secure Tourism program, the following equipment is required:
For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.
Assessment of skills acquired during the Training Bug Bounty 2026 - Hunt Vulnerabilities to Secure Tourism program is performed through:
Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.
Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.
Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.
No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.
Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.
A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certifiedPentesting & ethical hackingIndustry-certifiedPentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Strategy & steeringIndustry-certifiedStrategy & steeringIndustry-certified
 Strategy & steeringIndustry-certified
 Strategy & steeringIndustry-certified
 Strategy & steeringIndustry-certified
 Strategy & steeringIndustry-certified
 Data analysis & BIIndustry-certified
 Data analysis & BIIndustry-certified
 Data analysis & BIIndustry-certified
 Data analysis & BIIndustry-certifiedData analysis & BIIndustry-certified
 Data analysis & BIIndustry-certified
 E-commerceIndustry-certifiedE-commerceIndustry-certifiedE-commerceIndustry-certifiedE-commerceIndustry-certifiedE-commerceIndustry-certifiedE-commerceIndustry-certified
Available on-site and remotely. Pick your city to see the local training center.
30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.