Training Security Testing - Securing Your JavaScript Applications

$1,155

  • 1 day
  • Onsite
  • 10 people max.
Ref: UAU574
10 people max.
$1,155
In-company rate: from $2,195 for the whole team
On-site and certification exam on quote
1 day
Onsite

Don't let this gap widen

Why this program matters

  • Companies neglecting JavaScript security testing expose themselves to critical vulnerabilities.

  • On average, a breach costs 4,45 millions de dollars according to IBM.

  • Developers without these skills see their progress stalled and their projects rejected by clients.

  • Failing to master these tests exposes your career to unnecessary risks and weakens your company's competitiveness against the competition.

  • Act now to secure your applications.

Imed BEN AMOR, Learni trainer · Development expert
Imed BEN AMOR

Learni trainer · Development expert

73%productivity gap
×3cost of inaction
Flag of the United StatesBuilt for US teams
Payment by wire transferEnhanced confidentialityPerfect for companies with 50 to 500 employeesScheduling to fit any time zone

Trusted by — schools, companies and industrial groups

40,842 programs · 25 countries

  • Aptar
  • ArcelorMittal
  • Equans
  • EDF
  • Ubisoft
  • Microsoft

Every program built with a dedicated engineer

  • OpenAI
  • Anthropic
  • Mistral AI
  • NVIDIA
  • Google
  • Amazon Web Services
  • Microsoft Dynamics 365
  • Salesforce
  • ServiceNow
  • SAP
  • Oracle
  • Cisco
  • Fortinet
  • Palo Alto Networks
  • Aruba
  • VMware
  • Red Hat
  • Databricks
  • Snowflake
  • OVHcloud
  • Notion
  • AMD
  • Apple

Companies: Aptar, ArcelorMittal, Equans, EDF, Ubisoft and Microsoft.

Security Testing training objectives

  • Master the fundamentals of security testing in a professional JavaScript context
  • Develop practical skills to identify common vulnerabilities
  • Design test scenarios tailored to modern frameworks like Next.js
  • Implement detection and remediation tools in an enterprise environment
  • Optimize the security of your TypeScript projects for lasting protection
  • Integrate certified best practices into your development processes

Security Testing curriculum: 1 module over 1 day

Module 1 : Theme: JavaScript Security Testing for Web Applications (OWASP ZAP, Postman, manual audits, real-world Next.js cases)

This intensive day immerses you in security testing applied to JavaScript development. You will explore OWASP principles, use OWASP ZAP and Postman to scan APIs, and conduct audits on Next.js and TypeScript projects. Practical exercises based on real business cases will enable you to identify XSS flaws and injections, produce detailed reports, and learn how to remediate identified vulnerabilities. The training emphasizes actionable deliverables for your professional projects.

How Security Testing skills are assessed

  • Interactive quiz on JavaScript vulnerabilities
  • Practical exercise on scanning and security reporting
  • Self-assessment of acquired skills

How the Security Testing course is taught

  • Identification of XSS and CSRF risks
  • Use of automated testing tools
  • Writing professional reports
  • Fixing vulnerabilities in Next.js code

Security Testing training: access and practical arrangements

The Training Security Testing - Securing Your JavaScript Applications program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.

The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.

Equipment required

For the smooth delivery of the Training Security Testing - Securing Your JavaScript Applications program, the following equipment is required:

  • Mac or PC computers, high-speed fiber internet, whiteboard or flipchart, projector or interactive touch screen (for remote sessions)
  • Training environments installed on workstations or accessible online
  • Course materials, hands-on exercises and complementary resources
  • Post-training access to materials and educational resources

For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.

* contact us for remote delivery feasibility** ratio varies depending on the program

Skills assessment methods

Assessment of skills acquired during the Training Security Testing - Securing Your JavaScript Applications program is performed through:

  • During training: case studies, hands-on labs and professional scenarios
  • End of training: self-assessment questionnaire and skills evaluation by the trainer
  • After training: completion certificate detailing acquired skills

Program accessibility

Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.

Enrollment terms and lead times

Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.

The Learni story

Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.

Our method

How Learni guarantees the quality of your Security Testing training

Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.

Step 1

Rigorous trainer selection

Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.

  • Triple validation: technical, pedagogical, sectoral.
  • Minimum rating 4.8/5 over the last 12 sessions.
Step 2

You meet the trainer beforehand

30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.

  • Live briefing on goals and team context.
  • Veto right — we swap the trainer for free if needed.
Step 3

Content tailored to your context

No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.

  • Hands-on cases drawn from your stack and projects.
  • Program co-written then validated by your team.
Step 4

Continuous quality follow-up

Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.

  • NPS, knowledge quizzes and skills self-assessment.
  • Satisfaction guarantee: fully satisfied or free rework.

A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
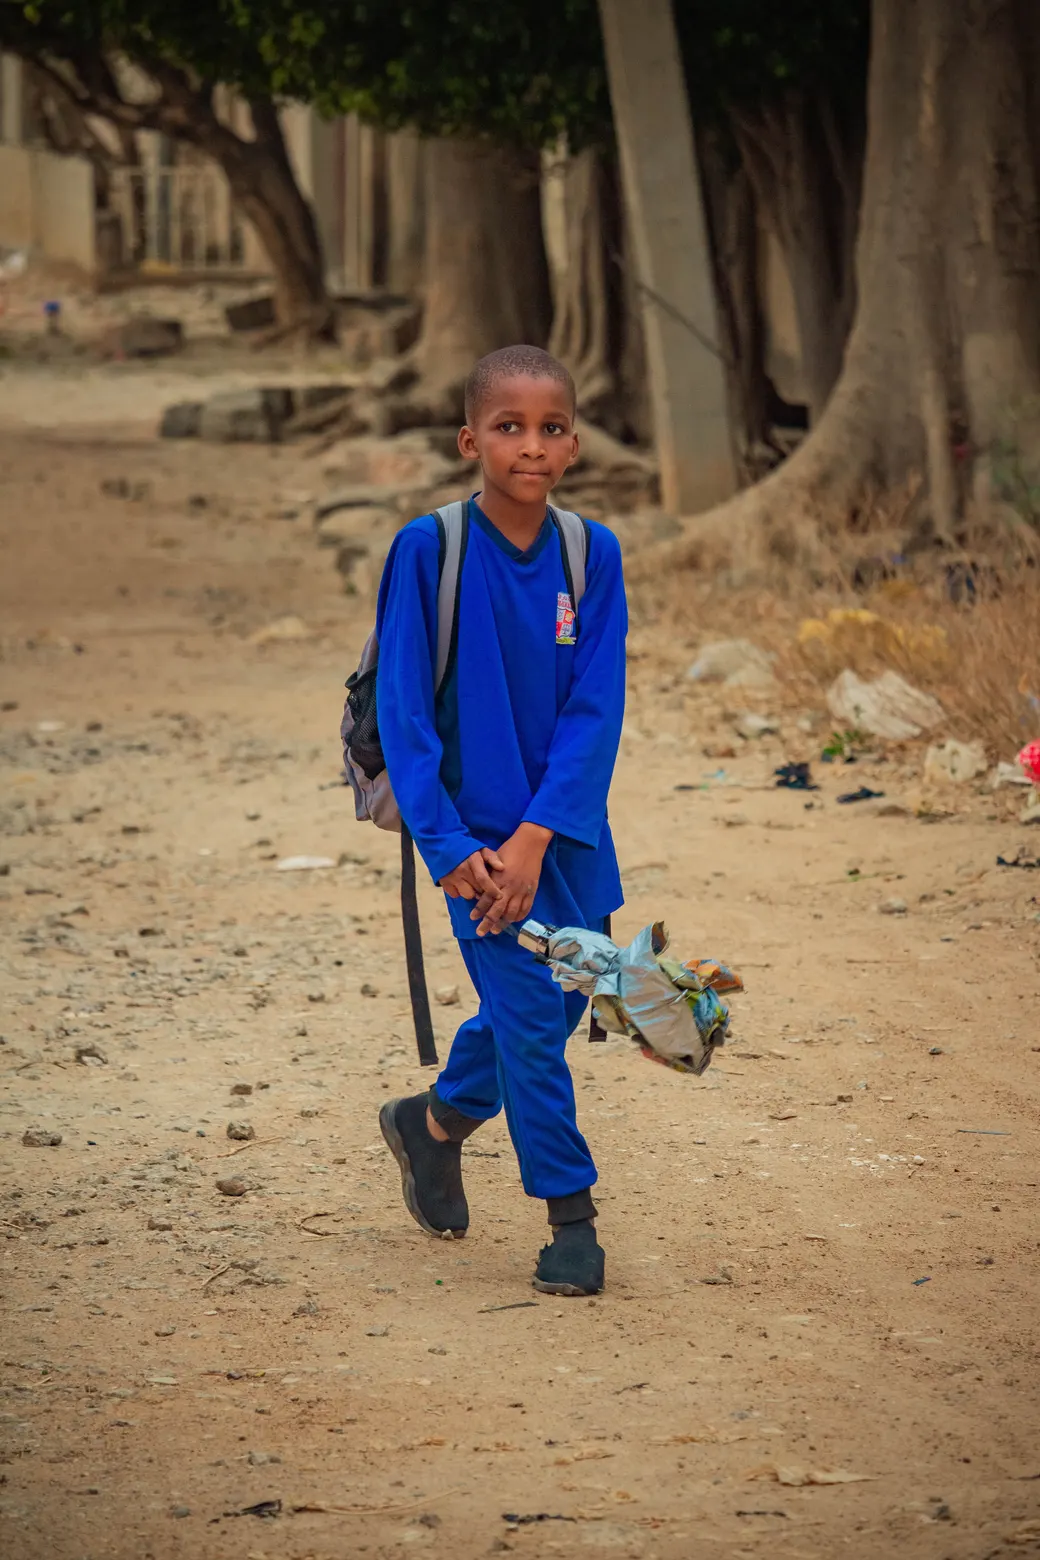
A child walking to school with a backpack
Our social commitment

A school kit donated to a child for every training booked

To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.

  • Backpack, notebooks and essential supplies
  • Distributed through our partner charities
  • Included, at no extra cost to you
Enroll and offer a kit
FAQ

Security Testing: frequently asked questions

Which tools are used in Security Testing training?+
Hands-on work runs on OWASP ZAP, postman, manual audits and real-world Next.js cases. Those tools come from the Security Testing program itself, delivered on site over 1 day, so participants practise on the stack they will use at work.
What can participants do after Security Testing training?+
They can master the fundamentals of security testing in a professional JavaScript context, develop practical skills to identify common vulnerabilities and design test scenarios tailored to modern frameworks like Next.js. Those are the stated objectives of the Security Testing program at Beginner level, checked by the end-of-session assessment.
How is Security Testing training assessed?+
Assessment relies on interactive quiz on JavaScript vulnerabilities, practical exercise on scanning and security reporting and self-assessment of acquired skills. Learni issues a completion certificate together with the individual assessment report at the end of the Security Testing program, which an L&D team can file as evidence.
How much does Security Testing training cost per participant?+
Security Testing training costs $1,155 per participant. For an in-company team, the flat rate starts at $2,195 for the whole group, up to 8 people. The detailed quote, sent within one business day, adjusts the amount to the format and how far the syllabus is tailored to your team.
How long does Security Testing training take?+
1 day, available live online (US time zones) or on-site at your offices. Half-day tracks spread over several weeks are possible so the team stays operational.
Who pays for Security Testing training?+
Most US teams pay directly through their company L&D or training budget. Learni invoices in US dollars and accepts bank transfer (ACH/wire) or card, with volume pricing for teams. A purchase order is welcome.
What do participants need to know before Security Testing training?+
Basic knowledge of JavaScript and web navigation; no prior testing tools required.
Is a certificate issued after Security Testing training?+
Yes. A Learni completion certificate is issued, along with the individual evaluation report. Learni is a certified training provider and prepares for third-party certifications, but does not award them itself.
Does Learni provide the equipment for Security Testing training?+
No. A computer and a stable internet connection are required for each participant. Learni provides the learning platform, the trainer and all course materials.
Your professional training, anywhere

Let's build your Security Testing learning path.

30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.
Reply within 24h · Vetted experts · USD invoicing · W-9 available
On-site & remote

Security Testing training in your city

Available on-site and remotely. Pick your city to see the local training center.

Share in 2 clicks