
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
- Triple validation: technical, pedagogical, sectoral.
- Minimum rating 4.8/5 over the last 12 sessions.

Describe your need, get a tailored program and a pre-filled quote in 3 min. A 100% free call with an advisor.

Trusted by — schools, companies and industrial groups
25,810 programs · 25 countries
Every program built with a dedicated engineer






Companies: Aptar, ArcelorMittal, Equans, EDF, Ubisoft and Microsoft.
Advanced installation and configuration of Burp Suite Professional in a secure environment, setup of transparent proxy with custom CA certificates, interception of complex HTTPS requests on real applications, practical exercises on vulnerable labs to analyze headers, cookies, and sessions, creation of custom filtering rules, real-time debugging of application flows with project scope, production of a first interception report to validate professional skills.
Exploration of Scanner modules for passive and active audits on OWASP Top 10, launching configured scans on multiple targets with engine tuning, analysis of results via dashboard with prioritization of critical vulnerabilities, use of Sequencer to test CSRF token and session quality, exercises on real enterprise cases involving SQLi and XSS, scan performance optimization for large volumes, generation of exploitation evidence for certification reports.
Mastery of Repeater for manually manipulating requests and responses in rapid iterations, configuration of Intruder with sniper, pitchfork, and cluster bomb attack positions on sensitive parameters, injection of custom payloads from databases like SecLists, measurement of responses via grep and timings to identify slow injections, practical workshops on auth brute-force and business logic flaws, recording of macros for complex attack chains, export of enterprise-usable results.
Discovery and installation of extensions via BApp Store for OOB and specific detections, use of Collaborator for out-of-band interactions with simulated C2 servers, integration of Burp with external tools like Metasploit via macros, writing structured reports with screenshot evidence and PoC, simulation of full pentest on enterprise red thread project, code review by the trainer, post-training action plan for recurring audits, delivery of certification templates.
The Training Burp Suite - Mastering Web Penetration Tests program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.
The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.
Equipment required
For the smooth delivery of the Training Burp Suite - Mastering Web Penetration Tests program, the following equipment is required:
For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.
Skills assessment methods
Assessment of skills acquired during the Training Burp Suite - Mastering Web Penetration Tests program is performed through:
Program accessibility
Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.
Enrollment terms and lead times
Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.
The Learni story
Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.
Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
You meet the trainer beforehand
30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.
Content tailored to your context
No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.
Continuous quality follow-up
Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.
A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
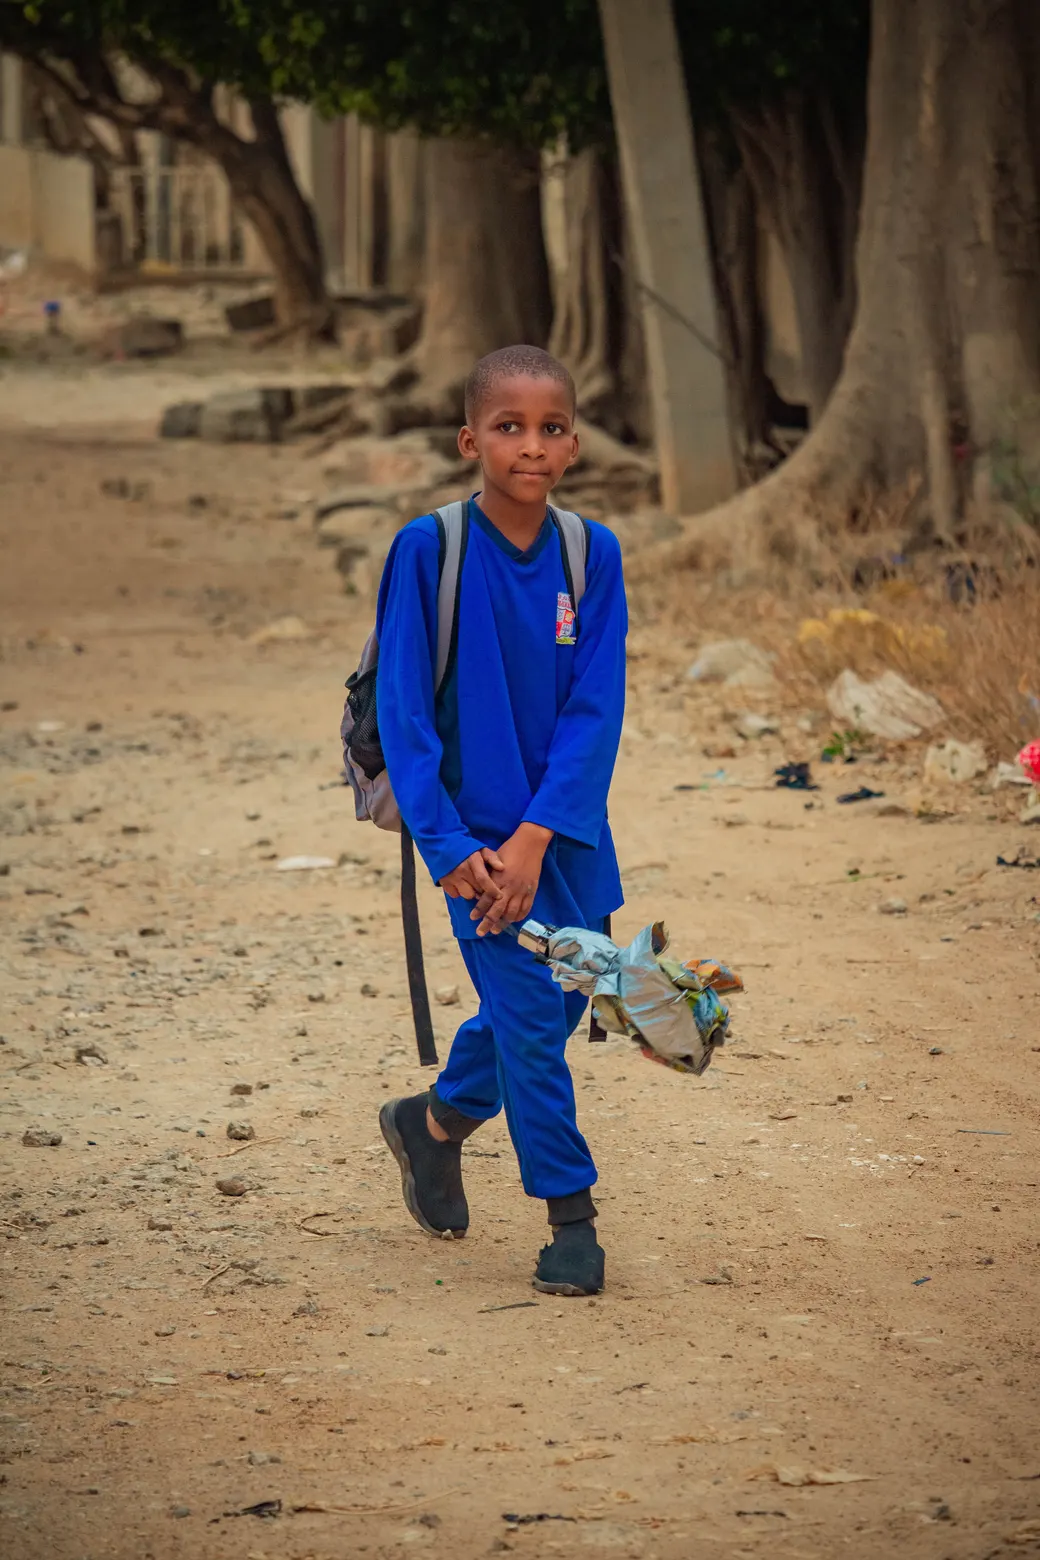
A school kit donated to a child for every training booked
To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.
30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.
 Security standards & governanceIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Application securityIndustry-certifiedApplication securityIndustry-certified
 Application securityIndustry-certified
 Operating SystemsIndustry-certifiedOperating SystemsIndustry-certified
 Operating SystemsIndustry-certified
 Cybersecurity fundamentalsIndustry-certifiedCybersecurity fundamentalsIndustry-certified
 Cybersecurity fundamentalsIndustry-certified
Available on-site and remotely. Pick your city to see the local training center.
We will call +1 (United States) 🇺🇸 — change the country code on the left if your number is from elsewhere.