
Rigorous trainer selection
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
- Triple validation: technical, pedagogical, sectoral.
- Minimum rating 4.8/5 over the last 12 sessions.

Describe your need, get a tailored program and a pre-filled quote in 3 min. A 100% free call with an advisor.

1 seat held for the next session
Request a call back and an advisor reaches you within 24 business hours, Monday to Saturday.
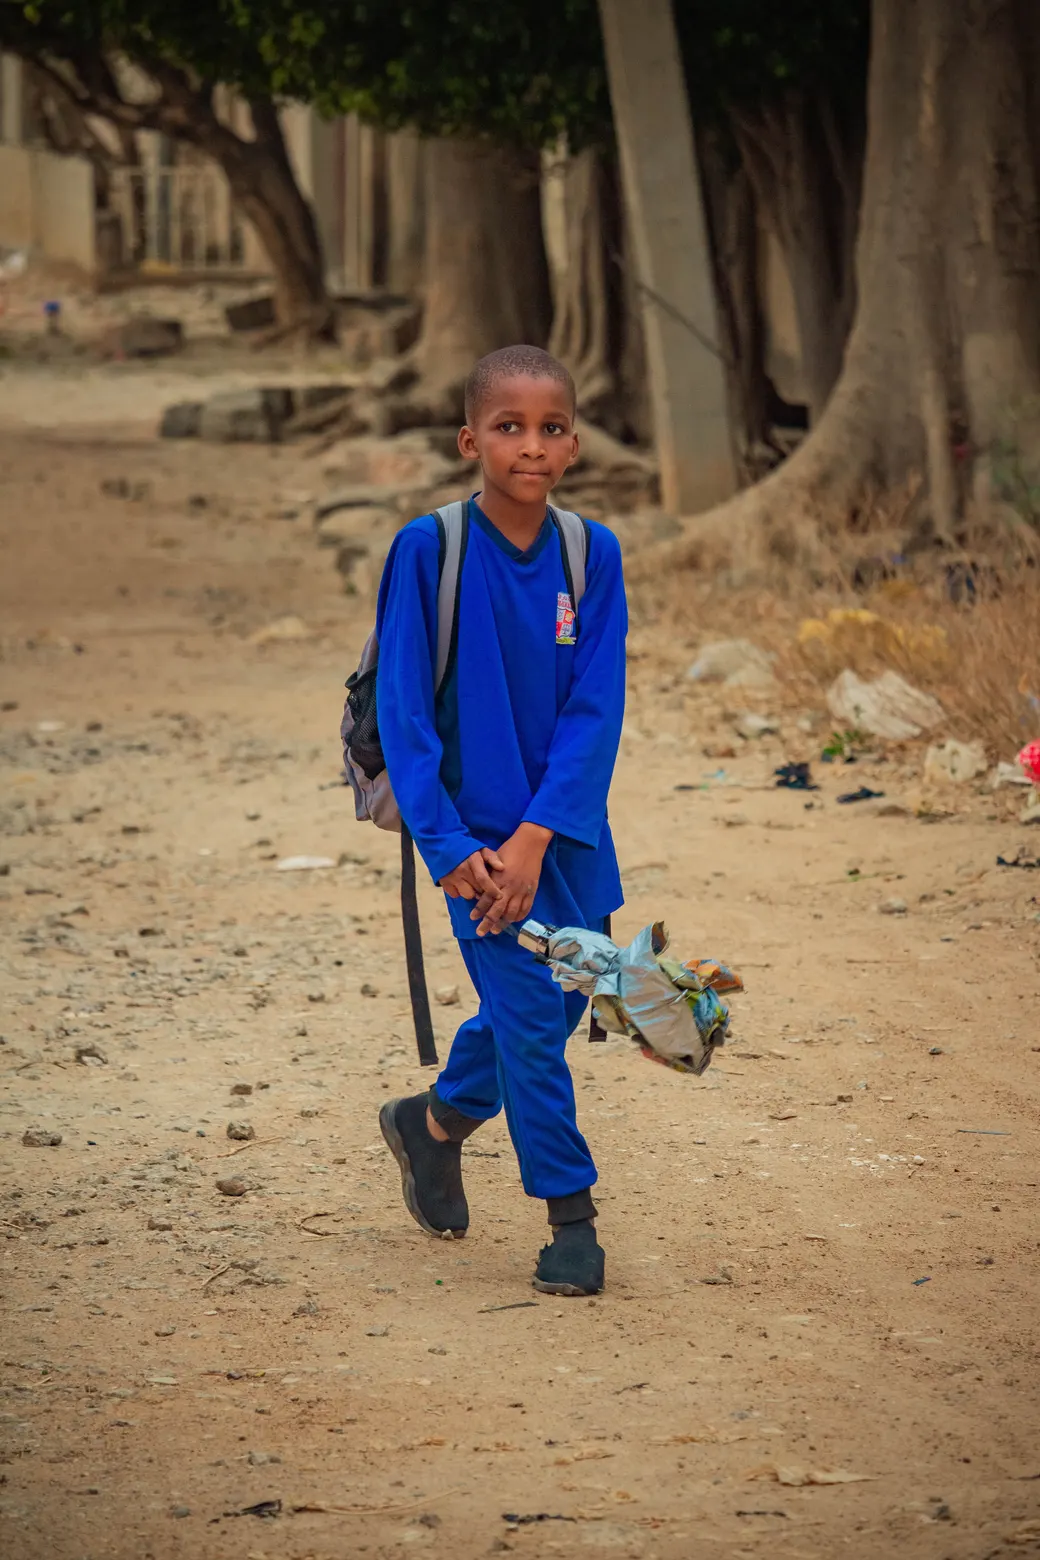
To fight inequalities in access to education, Learni donates a complete school kit to a child in need for every training booked. You build your skills, a child heads back to school.
Founded by engineers and learning experts, Learni's mission is to make high-impact tech training accessible to teams everywhere. We work remotely with organizations across the US and Canada, in your time zone, to help teams upskill fast.
Don't let this gap widen
Without bug bounty skills, companies suffer 70% of breaches from undetected vulnerabilities, costing an average of 4 million euros per incident according to IBM.
Security teams lose 50% of their time on manual false positives, delaying deployments and exposing the business to GDPR fines up to 4% of revenue.
In 2024, 85% of cyber job postings require bounty experience, sidelining stagnant profiles.
Every quarter without training widens the competitive gap against pro hunters who monetize millions.
Immersion in leading platforms like HackerOne and Bugcrowd, precise definition of scopes and rules of engagement, hands-on with Amass for passive information gathering on real targets, Burp Suite configuration for traffic interception and analysis, practical exercises on live programs to identify hidden assets, creation of an attack mind map with deliverable of an initial recon report.
In-depth exploration of OWASP Top 10 vulnerabilities adapted to bug bounty, use of FFUF for parameter and endpoint fuzzing, automated tests with Nuclei on custom scripts, manual exploitation of SSRF and IDOR on simulated enterprise labs, vulnerability chaining for high impacts, development of custom payloads during timed exercises, production of a video proof-of-concept to validate each discovery.
Writing professional reports compliant with program standards, structuring with CVSS scoring and clear reproduction steps, use of HackerOne templates to save time, simulation of responsible disclosures and bounty negotiations, review of real paid cases up to 50k$, exercises on your red thread project with expert feedback, action plan to integrate bug bounty into a certifying professional routine.
The Training Bug Bounty - Detecting Critical Vulnerabilities program is delivered onsite or remote (blended-learning, virtual classroom, remote presence). At Learni, an industry-certified training organization, every program is built to maximize skills acquisition regardless of the chosen format.
The trainer alternates between demonstrative, interrogative and active methods (through hands-on labs and/or scenarios). This pedagogical approach guarantees concrete learning that's immediately applicable at work.
For the smooth delivery of the Training Bug Bounty - Detecting Critical Vulnerabilities program, the following equipment is required:
For intra-company training on a site outside Learni, the client commits to providing all required teaching materials (computers, internet, etc.) for the smooth delivery of the program in line with the prerequisites in the communicated program.
Assessment of skills acquired during the Training Bug Bounty - Detecting Critical Vulnerabilities program is performed through:
Learni is committed to making its programs accessible. All our programs are accessible to people with disabilities. Our teams are available to adapt the pedagogical methods to your specific needs. Please contact us for any adjustment request.
Registration is possible up to 48 business hours before the start of training. All our programs are built for corporate L&D budgets and delivered onsite or remotely.
Before, during, after: we frame the brief, introduce the trainer, tailor the content and measure impact. You stay in control from kickoff to wrap-up.
Each trainer is validated on three criteria: hands-on field expertise, proven pedagogy and alignment with your industry.
30-minute video call between you and the selected trainer to validate the fit, adjust content and clear any final doubts.
No recycled slides. The syllabus is reworked from your real cases: tools, constraints, vocabulary, ongoing projects.
Live evaluations, 30/90/180-day check-ins and a consolidation plan. If the impact misses the mark, we rework it.
A simple promise: you don't pay to discover the trainer on day one. Everything is validated upfront, by you.
 Security standards & governanceIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Security standards & governanceIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Pentesting & ethical hackingIndustry-certified
 Security standards & governanceIndustry-certified
 Security standards & governanceIndustry-certifiedSecurity standards & governanceIndustry-certifiedSecurity standards & governanceIndustry-certified
 Security standards & governanceIndustry-certifiedSecurity standards & governanceIndustry-certifiedNetworking & telecomsIndustry-certifiedNetworking & telecomsIndustry-certifiedNetworking & telecomsIndustry-certifiedNetworking & telecomsIndustry-certified
 Networking & telecomsIndustry-certifiedNetworking & telecomsIndustry-certifiedCybersecurity fundamentalsIndustry-certifiedCybersecurity fundamentalsIndustry-certified
 Cybersecurity fundamentalsIndustry-certifiedCybersecurity fundamentalsIndustry-certified
 Cybersecurity fundamentalsIndustry-certified
 Cybersecurity fundamentalsIndustry-certified
Available on-site and remotely. Pick your city to see the local training center.
30 minutes with a learning advisor. No commitment. No sales pitch dressed up as a demo.